Data Migration Projects in the UAE: Prove Every Record Arrived Correctly
A UAE data migration guide covering inventory, ownership, mapping, cleansing, rehearsal, validation, reconciliation, cutover, privacy and defensible retirement.
The short answer
A data migration is complete only when the destination can support the intended business operations and every important record, relationship, total and permission has been validated. Inventory the source, assign field ownership, define transformation rules, rehearse with representative volume, reconcile independently and keep a controlled rollback or recovery path through cutover.
Weighing this for your business? Request a project review
Our take
Axiom Forge treats migration as a product and evidence programme, not a one-time import. The destination must be trustworthy enough for real decisions, support and future change.
Three choices to settle first
INVENTORY
Know what exists
Catalogue records, relationships, quality, retention, permissions and every consumer before mapping.
PROOF
Validate several ways
Combine counts, totals, checksums, relationship tests, samples and business journey validation.
CUTOVER
Control the transition
Rehearse synchronization, decision authority, recovery, communications and old-system retirement.
In this article6 sections · 4 min
A migration should begin with the business journeys the destination must support: serve a customer, settle an order, produce a required report, enforce access or investigate a historical decision. This turns correctness into testable outcomes rather than a statement that a file imported successfully.
Identify the required history, active records, attachments, relationships, audit events and permissions. Some data may be legally or operationally required but unsuitable for everyday search. Some duplicated or obsolete records should not be carried forward without purpose. Retention and deletion decisions need qualified legal input for the organisation’s context.
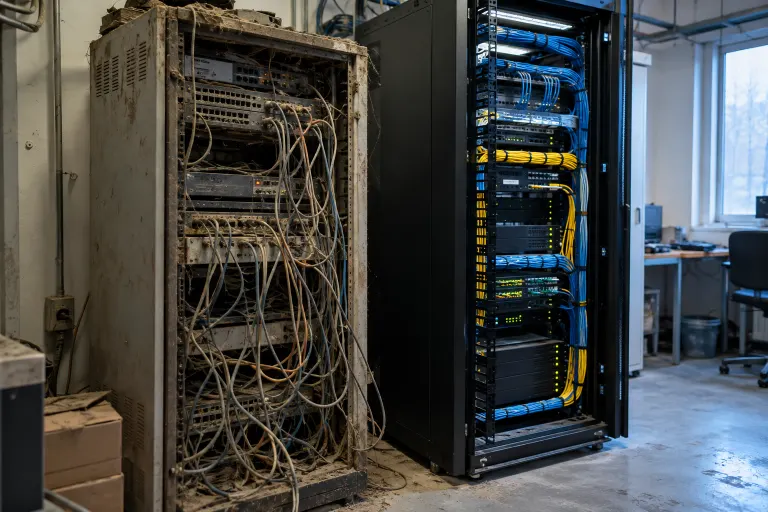
Catalogue databases, files, document stores, reports, exports and downstream integrations. Record technical owner, business owner, volume, growth, quality, classification and last successful backup. Include spreadsheets and locally maintained reference lists that correct or enrich the official system.
Trace who consumes each field and why. A code that appears unused may determine a financial report; a free-text note may contain personal data that should not be copied. NIST’s data-integrity guidance emphasizes knowing and protecting enterprise assets against corruption and destructive events. That inventory discipline is equally valuable during planned change.
Define source field, destination field, owner, transformation, default, validation and treatment of invalid values. Preserve original identifiers or a durable cross-reference so teams can investigate differences after cutover. Do not collapse several meanings into one clean-looking destination status without documenting the decision.
Separate cleansing from migration logic where possible. Correct known source issues through governed rules and preserve a report of changes. Values that cannot be resolved should enter an owned exception queue rather than being silently dropped or replaced with a default that looks valid.
| Layer | Example evidence | Owner |
|---|---|---|
| Structure | Type, length and required constraint | Data engineering |
| Meaning | Business definition and valid states | Process owner |
| Transformation | Versioned rule and exception treatment | Joint review |
| Outcome | Journey and report validation | Business acceptance |
Run the complete extraction, transformation, loading and validation process in a production-like environment. Include peak volume, large attachments, old encodings, duplicate identities, missing references and records changed during the migration window. Measure duration and resource needs rather than estimating from a small sample.
Protect test data appropriately. Use minimization or representative synthetic data when full personal records are not required, and restrict migration tooling plus temporary exports. The UAE data-protection framework includes obligations around personal-data processing, security and cross-border transfer that should be evaluated for the chosen environment and suppliers.
Use independent checks: record counts by meaningful segment, financial totals, checksums, relationship integrity, duplicate exposure, permission tests and representative samples. Confirm that reports and operational journeys produce expected results. A count can match while values are attached to the wrong customer or state.
Record every validation, tolerance, reviewer and result. Resolve differences or approve a documented exception before cutover. Keep a reproducible reconciliation report after launch because delayed consumers and month-end processes may reveal issues not visible in the first day of use.
Decide whether the source will freeze, continue synchronizing or accept a limited set of changes. Define the final delta process, rollback trigger, decision authority, support staffing and communication plan. Rehearse restoration and confirm that a rollback would not lose records created after the switch.
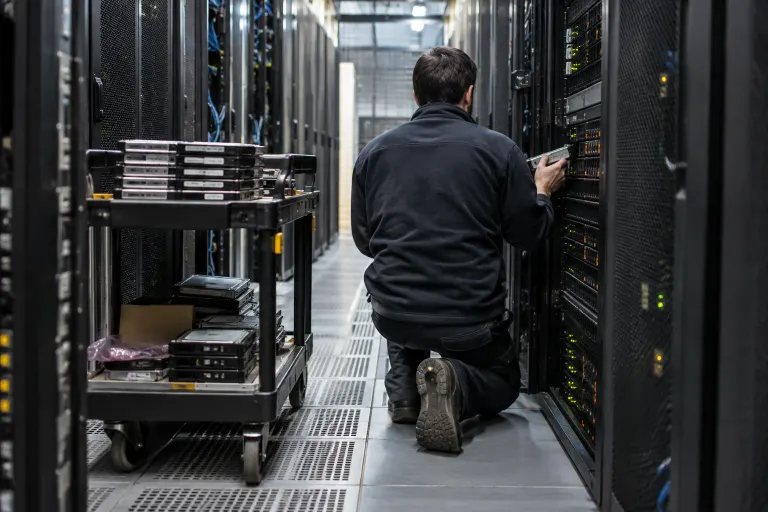
Axiom Forge recommends retiring the old platform only after destination operations, audit needs, integrations, archives and access controls are proven. Remove obsolete credentials and temporary migration stores. Success is not a copied database; it is a trusted operating system with evidence that the transition preserved what the business needs.
Discuss your project with the founder
How do we validate a data migration?
Combine counts, totals, checksums, relationship checks, permission tests, sampled records and end-to-end business journeys. Document tolerances, owners and unresolved exceptions before approval.
Should all legacy data be migrated?
Not automatically. Decide from operational need, legal retention, audit value, quality and cost. Some records may belong in a protected archive rather than the active production model.
Can a migration happen with little downtime?
Often, using staged loads and a controlled final delta, but the feasible approach depends on transaction volume, source capabilities, consistency requirements and whether old and new writes can be reconciled safely.
- NIST — Data Integrity: Identifying and Protecting Assetscsrc.nist.gov (opens in a new tab)
- UAE Government — Data protection lawsu.ae (opens in a new tab)
- NIST — Secure Software Development Frameworkcsrc.nist.gov (opens in a new tab)
- TDRA Digital Government — API First Guidelinedgov.tdra.gov.ae (opens in a new tab)