Legacy Software Modernization in the UAE: Change Without Losing Control
A UAE guide to modernizing legacy software through dependency mapping, staged replacement, secure delivery, migration controls and measurable operating outcomes.
The short answer
Modernization should reduce operational risk before it replaces every old component. Start by mapping business-critical journeys, data ownership, integrations, manual workarounds and failure costs. Put an observable boundary around the legacy system, move one valuable capability at a time and keep reconciliation plus rollback available until the new path has proved reliable.
Weighing this for your business? Request a project review
Our take
Axiom Forge does not treat a rewrite as progress by itself. The useful outcome is a system the business can change safely, understand operationally and support without depending on hidden knowledge inside one application or one person.
Three choices to settle first
BOUNDARY
Map the operating system
Document journeys, dependencies, owners, data and failure impact before deciding which code should move first.
SEQUENCE
Replace one capability
Use a staged boundary so the old and new paths can coexist while evidence accumulates.
CONTROL
Reconcile every transition
Keep explicit state, observability, rollback and named operational ownership through cutover.
In this article6 sections · 5 min
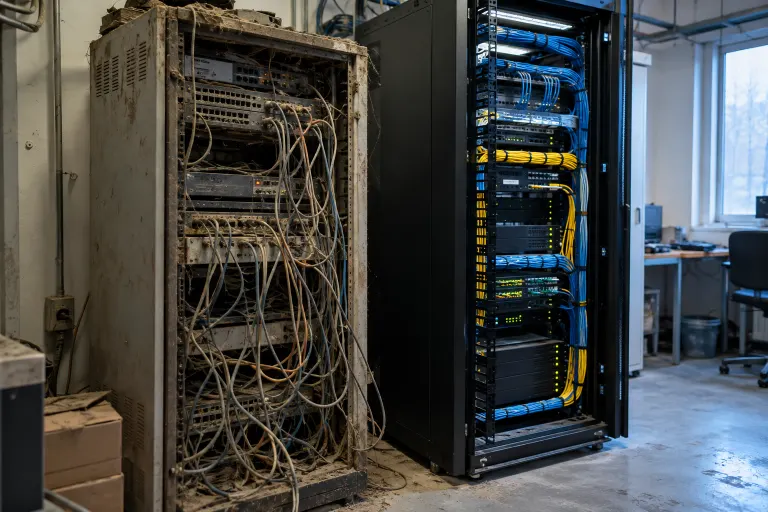
Legacy software is not automatically a problem because it is old. It becomes a commercial risk when changes take too long, important knowledge is undocumented, support has ended, integrations fail silently or ordinary growth requires dangerous manual work. Build the case from delayed revenue, service interruptions, correction effort, security exposure and the cost of keeping specialist knowledge available.
Separate the symptoms by capability. A weak reporting module does not justify rewriting dependable transaction logic. An unsupported public-facing component may deserve immediate isolation even if users like its interface. The UAE Digital Economy Strategy signals long-term national investment in digital capability, but an individual company still needs a precise operating reason for each modernization decision.
Create an inventory of applications, databases, scheduled jobs, file exchanges, vendor services, user roles and downstream reports. Then interview the people who recover failed records, repair spreadsheets and explain exceptions to customers. Those unofficial steps are part of the real system even when they do not appear in architecture diagrams.
Trace a small number of high-value journeys from input to final business state. Record identifiers, timing, approval, reconciliation and the owner of each failure. This identifies where a clean interface can be introduced and where a hidden dependency would make an early cutover unsafe. Treat production data and configuration as assets that need the same attention as source code.
A staged replacement often begins with a stable interface around the legacy capability. New requests pass through that boundary, which records behavior and can gradually route selected cases to a new service. Start with a capability that has meaningful value, understandable rules and recoverable errors. Avoid beginning with the largest or most politically visible module merely because leadership wants a dramatic milestone.
Use parallel runs or shadow reads where appropriate. Compare old and new outcomes using durable identifiers and agreed tolerances. The old path should remain available until exceptions, volume and support behavior are understood. A deadline can focus delivery, but a cutover date is not evidence that the new operating model works.
| Stage | Primary evidence | Promotion condition |
|---|---|---|
| Observe | Journey and failure baseline | Owners agree on current state |
| Wrap | Stable contract and logs | Requests are traceable end to end |
| Shadow | Old/new comparison | Differences are understood |
| Route | Controlled live cohort | Errors are detectable and recoverable |
| Retire | Dependency and archive proof | No required consumer depends on the old path |
Modernization should not copy every historic permission and dataset into a cleaner interface. Reconfirm who needs each data field, action and report. The UAE federal personal data framework defines responsibilities around processing, security, correction and cross-border transfer; the precise legal position should be reviewed for the organization, sector and free-zone context.
Integrate secure development practices into the delivery plan. NIST’s Secure Software Development Framework provides a useful common vocabulary for security requirements, protected development environments, provenance and vulnerability response. Legacy risks should not be exchanged for hurried new code, broad service accounts or undocumented third-party components.
Write the cutover runbook before the final week. It should identify the data freeze or synchronization method, validation queries, decision authority, customer communications, support escalation, rollback trigger and the treatment of records created during an interrupted transition. Rehearse it with realistic data volumes and dependency failures.
After release, observe completion rate, correction rate, latency, unresolved exceptions and support effort by journey. Keep responsibility visible across business and engineering teams. Decommission only after archives are verifiable, integrations have moved and access to the old platform can be removed without erasing evidence the company must retain.
A useful first phase produces a system map, journey baseline, risk register, target boundaries, migration approach, security requirements and a release sequence tied to business outcomes. It should also expose which assumptions require a technical spike or data sample before a reliable investment range can be produced.
Axiom Forge recommends selecting one end-to-end capability and the minimum platform work needed to support it. The output should leave the organization with a clearer architecture and operating model even if later phases change. Avoid proposals that promise a total rewrite before anyone has inspected production dependencies or defined how correctness will be proven.
Discuss your project with the founder
Should a UAE business rewrite its entire legacy system?
Usually not as a first assumption. A capability-by-capability assessment can preserve dependable parts, isolate urgent risks and create evidence before the organization commits to a full replacement.
Can modernization happen without stopping operations?
Often yes, through controlled coexistence, parallel validation and staged routing. The feasibility depends on data ownership, transaction boundaries, integration behavior and the ability to reconcile old and new states.
What should be measured after a legacy system release?
Measure successful business completion, correction and exception rates, response time, support effort, security findings and the time required to make a safe change—not only uptime or lines of code moved.